You push to a private repo from a conference Wi-Fi network, SSH into a staging box from a train, and paste an API key into a terminal at a cafe. Most developers do all three in a single week without thinking about the network underneath. A VPN is the usual fix, but the usual fix has a weak spot: you're asked to trust the provider's word. VP.net takes a different route, and a detailed vp.net review explains why that matters if you care about how a privacy claim is enforced rather than how it's worded.
Why Developers Have a Bigger VPN Problem Than Most
A regular user risks a stolen streaming login. A developer's laptop holds SSH keys, cloud console sessions, personal access tokens, .env files, and database credentials. One intercepted session can lead to a production environment, not just a single account.
Dev work also happens in awkward places: co-working spaces, hotel rooms, client offices, airports. Each one is a network you didn't configure and can't audit. Encrypting your traffic before it leaves the machine is a cheap control, and it works regardless of which tools you run on top.
What a VPN Does and Doesn't Cover
It helps with:
Untrusted Wi-Fi. Traffic is encrypted between your device and the VPN server, so other people on the network can't read it.
IP exposure. Services you connect to see the VPN server's address instead of yours.
Geo-testing. You can check how a site, CDN, or API behaves from another region.
It does not help with:
Phishing or malware. A VPN doesn't stop you from running a bad script.
Weak credentials. Reused passwords stay reused.
Leaky applications. An app that sends secrets in plain text over its own channel is still a problem.
Keep that boundary clear and a VPN becomes one layer in a stack, not a magic fix.
The Trust Problem With "No-Logs"
Almost every provider advertises a no-logs policy. As an engineer, you already know what that is: a statement, not a mechanism. You can't inspect the server, read the code running on it, or confirm the config matches the policy. Audits help, but an audit is a snapshot of one day, not a guarantee about every day after.
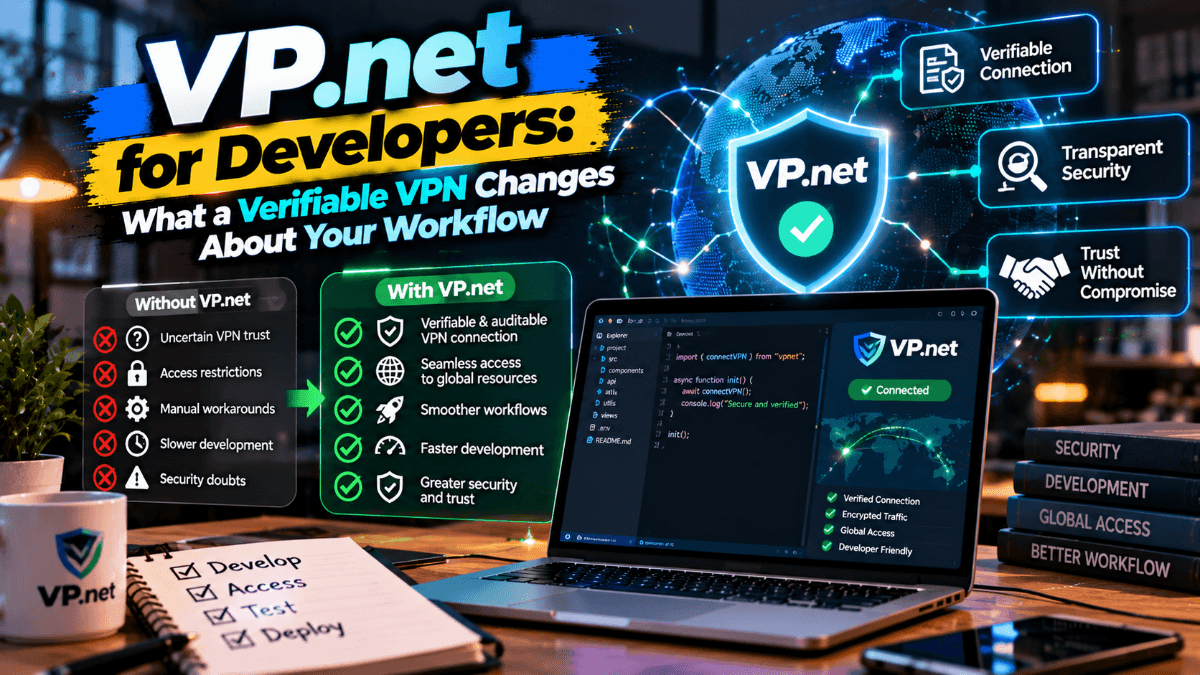
That is the gap vp.net is built to address. Instead of asking users to believe a policy, it uses hardware-based isolation, specifically Intel SGX enclaves, so the code that handles your connection runs in a protected environment the operator cannot read into. Combined with remote attestation, the idea is that a client can check that the server is running the expected, published software before it sends any traffic.
For anyone who has ever written a threat model, the difference is easy to see. "We promise not to look" is a trust assumption. "The hardware prevents us from looking, and you can verify the software" is a smaller one.
How the vp.net Approach Compares to a Standard VPN
How is no-logs enforced?
- Typical VPN: Policy and occasional audits
- vp.net approach: Hardware isolation plus attestation
Can you verify the running code?
- Typical VPN: Rarely
- vp.net approach: That is the design goal
What must you trust?
- Typical VPN: The company and its staff
- vp.net approach: Hardware and published code
Failure mode
- Typical VPN: A policy broken quietly
- vp.net approach: A check that fails visibly
No design removes trust entirely. SGX has had its own research-reported vulnerabilities over the years, and you are still relying on the hardware vendor. The practical point is that vp.net narrows what you have to trust and gives you a way to check part of it, which is more than most providers offer.
Testing Any VPN Before You Rely On It
Whichever provider you pick, test it. A few minutes catches most problems.
Check your public IP before and after connecting.
curl -s https://ifconfig.me
- The address should change when the tunnel is up.
- Check for DNS leaks. Run a lookup and confirm the resolver belongs to the VPN, not your ISP or the local network.
- Check IPv6. A tunnel that handles IPv4 but ignores IPv6 can leak your real address.
- Kill the connection on purpose. Disable the VPN mid-transfer and confirm the kill switch stops traffic instead of falling back to the open network.
- Run a throughput test against a server you actually use, such as your git host or cloud region, not just a generic speed site.
A vp.net review is also worth reading alongside your own testing, since it covers the architecture claims that a speed test can't show you.
Practical Habits That Pair Well With a VPN
Keep secrets out of shell history. Use a password manager or a secrets tool, not pasted tokens.
Use hardware keys or SSH agents with short-lived credentials where you can.
Separate work and personal browser profiles, so a cafe session doesn't mix with production consoles.
Turn on the VPN by policy, not by mood. If it's off half the time, it protects half the time.
Final Thoughts
Developers are better placed than most to judge a security claim, because they know the difference between a promise and a mechanism. vp.net is worth a look for exactly that reason: it tries to turn a privacy promise into something you can check. Test it like you'd test any dependency, read the architecture notes, and decide whether the smaller trust surface fits your threat model. If it does, you've swapped a policy page for a design you can reason about.